
Germany Warns Over Six Unpatched Flaws in Danfoss Refrigeration Controllers
Germany's BSI says Danfoss AK-SM800A refrigeration controllers should not be on the internet after six unpatched flaws were found, and the newest firmware may not fix them. Who is affected and what IT teams should check with facilities.
 KBY News Desk
In this article
Table of Contents
Table of contents
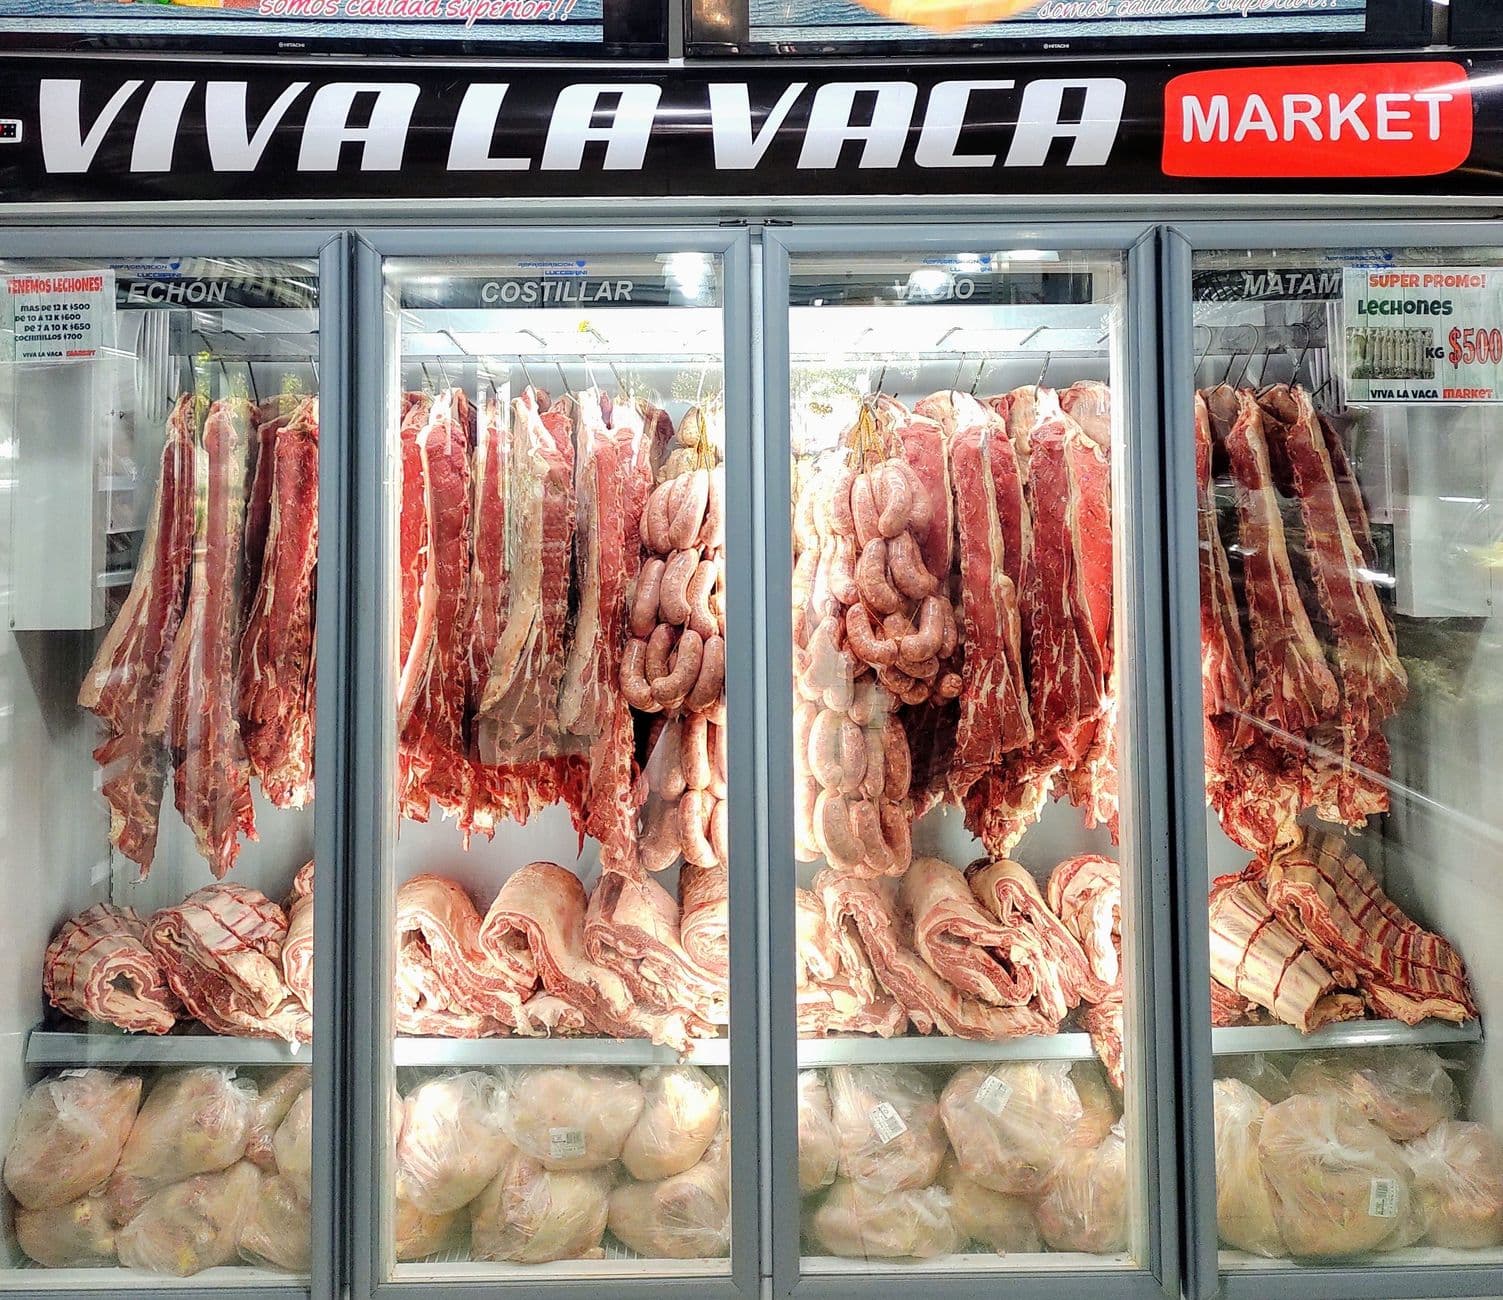
Germany’s Federal Office for Information Security (BSI) warned on Friday 13 November that six unpatched flaws in Danfoss AK-SM800A refrigeration controllers, the system managers that run cold rooms and display cases in many supermarkets and food businesses, are serious enough that the devices should not be connected to the internet at all. The flaws were found by Carlo Meijer of the Dutch security firm Midnight Blue. They affect firmware up to and including version 5.3.2, have no CVE numbers yet, and have no confirmed fix: Danfoss has released firmware 5.4.0, but Midnight Blue says it does not patch them, and the BSI corrected its own advice the same day to say that 5.4.0 being affected “cannot be ruled out”. The BSI says it knows of no attacks using these flaws so far.
We are covering this three days after the BSI’s warning because it reached most English-language outlets late, and because the advice is simple and urgent for anyone whose organisation runs refrigeration plant: find these controllers and take them off the internet.
#What the AK-SM800A is, and why IT should care
The AK-SM800A is a system manager: a box in the plant room or back office that supervises a site’s refrigeration, collects temperatures and alarms, and lets engineers change settings and run defrost cycles remotely. That remote access is the problem. Refrigeration contractors often connect these units to the internet directly, or through a 4G or 5G modem in the cabinet, so that they can reach them from anywhere. The device then sits outside the corporate network, outside IT’s asset list and outside its patching, even though it controls equipment that holds stock worth a great deal of money and, in food businesses, matters for safety.
That is why this belongs on an IT team’s desk even when facilities owns the kit. The question “do we have any of these on the internet?” is one IT is usually best placed to answer.
#What Midnight Blue found
Midnight Blue describes the flaws as “Multiple (6) stack-based buffer overflows” and says Meijer found them “within an hour of manual investigation”. According to The Hacker News, five sit in web handlers that answer without a login and run as root, and the sixth is in the gateway that enforces the controller’s Strict mode, the setting meant to lock it down.
In practical terms, Midnight Blue says an attacker could “change parameters or initiate unwanted actions (such as defrosting operations)”. It also notes that the devices “do not make use of the i.MX6’s secure boot features”, which means an attacker who gets in could leave code that survives a reboot or render the unit unusable. Its demonstration of remote code execution ran on older 3.3.0 firmware, and it says the same bugs are present in 5.3.2.
Midnight Blue says it will “withhold technical details until disclosure is sorted”. That holds back the details an attacker would need, but it also means there is nothing yet for defenders to check against, apart from the version number.
#What the BSI and Belgium’s CCB said
The BSI’s press release, issued in Bonn on 13 November, is blunt. “Betroffene Geräte sollten nicht mit dem Internet verbunden werden,” it says: affected devices should not be connected to the internet. Where remote access is unavoidable, it “rät das BSI Betreibern dringend dazu, zumindest ein Virtual Private Network (VPN) vorzuschalten”: the BSI urgently advises operators to put at least a VPN in front of them. It says firmware “bis mindestens 5.3.2” (up to at least 5.3.2) is affected, and that nothing is currently known about active exploitation of the flaws.
Its first version said firmware 5.4.0 was not affected. An update the same afternoon withdrew that: “Dies kann zum jetzigen Zeitpunkt jedoch nicht ausgeschlossen werden” (this cannot be ruled out at this time). Midnight Blue goes further. In an update reported by the trade publication Cooling Post, it says 5.4.0 does not patch the flaws, and that “according to the file timestamp this firmware was likely built on October 29”.
Belgium’s Centre for Cybersecurity (CCB) issued its own warning a day earlier. Cooling Post reports that the CCB advised removing direct public internet exposure of AK-SM800A controllers, and said that updates, password changes and Strict mode are “insufficient on their own”. The Hacker News reports that Ireland’s National Cyber Security Centre gave the same advice.
#The background: attacks on fridge controllers across Europe
These flaws arrive in the middle of a wave of attacks on refrigeration controllers. Midnight Blue says attacks on “internet-exposed fridge controllers by Danfoss and Copeland throughout Europe” began on 11 October, with a second wave on 2 November, and that public exploit code for older Danfoss flaws appeared within 48 hours of the attacks on French supermarkets. In the United States, CISA and four other federal agencies published guidance on 5 November saying they were “aware of malicious cyber activity targeting industrial refrigeration and cold chain monitoring systems globally”, and their first recommendation is to “Eliminate public internet exposure”.
It is important to be clear about what is not known. Nobody has linked the six new flaws to those attacks: The Hacker News reports that neither the agencies nor the researchers do, and the public exploit code Midnight Blue mentions was for older Danfoss flaws. Midnight Blue says “attribution remains open”. What the attacks show is that people are already looking for exposed refrigeration controllers and acting on what they find, and that makes six new, unpatched ways in more dangerous than they would otherwise be.
#Our view: patching is the wrong first move
For most security flaws, the advice is to patch. Here, in our view, it is the wrong place to start, for three reasons. There is no patch that anyone has confirmed works. The vendor’s newest firmware may still be vulnerable, by the BSI’s own correction. And even a working patch would not help a device that an attacker can reach from anywhere, run old firmware on, and fail to secure-boot.
Midnight Blue puts it more sharply, calling a patch-first response “a misallocation of scarce security and personnel resources” and saying “asset owners need to remove internet exposure as soon as possible”. We agree. A refrigeration controller has no business answering connections from the whole internet. The engineer who needs remote access can reach it through a VPN or a private mobile network; nobody else should be able to reach it at all.
We think the harder part is organisational, not technical. These units are often installed and maintained by refrigeration contractors, connected by them, and invisible to IT. The first job is finding out whether you have them and how they are connected, and that usually means a conversation with facilities and the contractor, not a scan of the corporate network.
#Who is affected
Any organisation running a Danfoss AK-SM800A on firmware up to 5.3.2, and possibly 5.4.0, that can be reached from the internet. That includes supermarkets and convenience stores, food manufacturers and distributors, cold stores, and any site with commercial refrigeration supervised by this model. A unit that is only reachable inside a private network is at much lower risk, though not none. Other Danfoss models are not named in the advisories.
#What to do
- Ask the question this week. Ask facilities and your refrigeration contractor whether any site uses a Danfoss AK-SM800A, what firmware it runs, and how it is reached remotely.
- Check for internet exposure. Look at your public IP ranges and any attack-surface monitoring for these devices, and ask the contractor specifically about 4G and 5G modems in plant cabinets, which do not appear on the corporate network at all.
- Take them off the internet. Where a controller is reachable directly, remove that access. If remote access is needed, follow the BSI’s advice and put it behind a VPN, a private mobile network or a tightly limited allow-list of addresses.
- Do not treat 5.4.0 as a fix. Update if your contractor recommends it, but do not count it as closing these flaws until Danfoss says so.
- Watch for changes. Unexpected defrost cycles, setpoint changes or a unit that stops responding should be reported to the contractor and treated as a possible incident, not just a fault.
#What happens next
We would expect CVE numbers and a Danfoss advisory once Midnight Blue and Danfoss agree on disclosure, and then the technical details. That is the point at which the risk rises sharply for any controller still on the internet, because the details will show attackers exactly where to aim. The time to remove exposure is before then.
Evidence trail
Sources and verification
Primary documentation and external technical references used in this article.
- 01BSI press release, 13 November 2026 (German)bsi.bund.de
- 02Midnight Blue: multiple RCE in Danfoss AK-SM800Amidnightblue.nl
- 03The Hacker News: six unpatched Danfoss refrigeration controller flawsthehackernews.com
- 04Cooling Post: Belgium warns of new Danfoss controller vulnerabilitiescoolingpost.com
- 05CISA: US government partners urge hardening of industrial refrigeration and cold chain monitoring systemscisa.gov
About this page
Credited to
Dates
Published
Corrections
No corrections are listed for this page. Some review sweeps corrected pages without naming each one; those are in the corrections log.
Read-only scripts
- Windows devices with no BitLocker recovery key in Entra IDMicrosoft Entra ID, Windows
- Intune devices that haven't synced in N daysMicrosoft Intune
- Mailboxes forwarding to external addressesExchange Online
- BitLocker status of every volume on this PCWindows
Upcoming deadlines
- Intune moves to macOS 15 and laterQ4 2026
- SAP SuccessFactors provisioning: move from basic auth to workload identityNovember 2026
- Intune November release: JIT registration reminder at APNs renewal and automatic JIT for eligible tenantsNovember 2026
Explore KBY
The KBY Brief
A short email about twice a week with new runbooks, configuration traps and fixes from KBY Technologies.
SubscribeMore news
All news
 Platforms and devices
Microsoft Previews Remote Lock for Lost Windows Devices in Intune
Was this useful?
Reports go to the site owner and are used to correct pages. Corrections are listed at /corrections.
Get new fixes by email.
New runbooks, configuration traps and fixes from KBY Technologies, about twice a week.
Comments
Add a thoughtful note on Germany Warns Over Six Unpatched Flaws in Danfoss Refrigeration Controllers. Comments are checked for spam and held for moderation before appearing.