
Equinor Says Its Cyberattack Is Still Under Way Three Days On, With Production Unaffected
Equinor, Europe's largest gas supplier, says the attack on its IT systems continues and recovery has no timeline. What its three statements say, what they leave out, and what customers and partners should check.
 KBY News Desk
In this article
Table of Contents
Table of contents
Equinor, the Norwegian energy company that The Register describes as Europe’s largest supplier of natural gas, said on Thursday 19 November that the cyberattack it first disclosed on Tuesday evening is still going on. Its latest statement, timed 11:40 Central European Time, says work to stop the attack and restore “full integrity” to the affected systems continues, that it is too early to say how long that will take, and that production is running as normal. It also says there are no indications that data has been stolen or altered.
That is the whole of what the company has put on the record, and it is a short list. We know the attack is on IT systems, not on the equipment that extracts and moves gas. We do not know what kind of attack it is, who is behind it, how long the attackers were inside, or when staff will have normal systems back.
#Three statements, read in order
Equinor has updated one page on its website three times, so the sequence is worth reading as a sequence. The original notice, at 18:55 on Tuesday 17 November, said it had detected “an ongoing cyber-attack against certain IT systems”, that resources had been mobilised to neutralise it, that there were no indications of data theft, and that operations and production were not affected.
The second, at 09:47 on Wednesday, said Equinor now had “a clearer understanding of how the attack was carried out and which systems have been affected”. It added: “As this is not a virus attack, there is no risk of the attack spreading.” It said there was no indication of consequences for employees, partners or suppliers. It still did not say how long recovery would take.
The third, on Thursday, adds that the attack “does not appear to be specifically targeting Equinor”, that the company is in continuous contact with national security authorities, and that it has reported the matter to the police. Equinor has not named an attacker, has not said whether any demand has been made, and has not described the method.
Equinor’s spokesperson, Ellen Maria Skjelsbæk, told the Norwegian news agency NTB that the company had not lost access to its IT systems, although staff might have trouble reaching some corporate applications and services, according to The Register. The Register adds that Reuters reported the company’s internal email system was down. We have not been able to confirm the email detail on Equinor’s own pages, so treat it as a report, not a confirmed fact.
#What “not a virus attack” probably does and does not tell you
This is our reading, labelled as such. Equinor’s reassurance that the attack cannot spread is a statement about malware that copies itself from machine to machine. It says nothing about whether an intruder is moving by hand, whether an account or a trusted connection has been abused, or whether a service Equinor relies on has been disrupted from outside. Plenty of serious incidents involve no self-spreading code at all: stolen credentials, an exposed remote access service, or a flaw in an internet-facing application can all give a person or an automated tool the run of a network.
The phrase “does not appear to be specifically targeting Equinor” is more interesting. We read it as the company saying the evidence points to something broader than a campaign aimed at one energy firm. That could mean a widely used product or service is being abused, or that attackers are working through a list of organisations. It could also be a cautious holding statement. Nothing in the public record lets us say which, and we are not suggesting any link to other incidents. We would simply note that if the cause turns out to be a shared weakness, other organisations may need to act quickly, and we will update this story if one is named.
#Why the production claim matters, and how far it goes
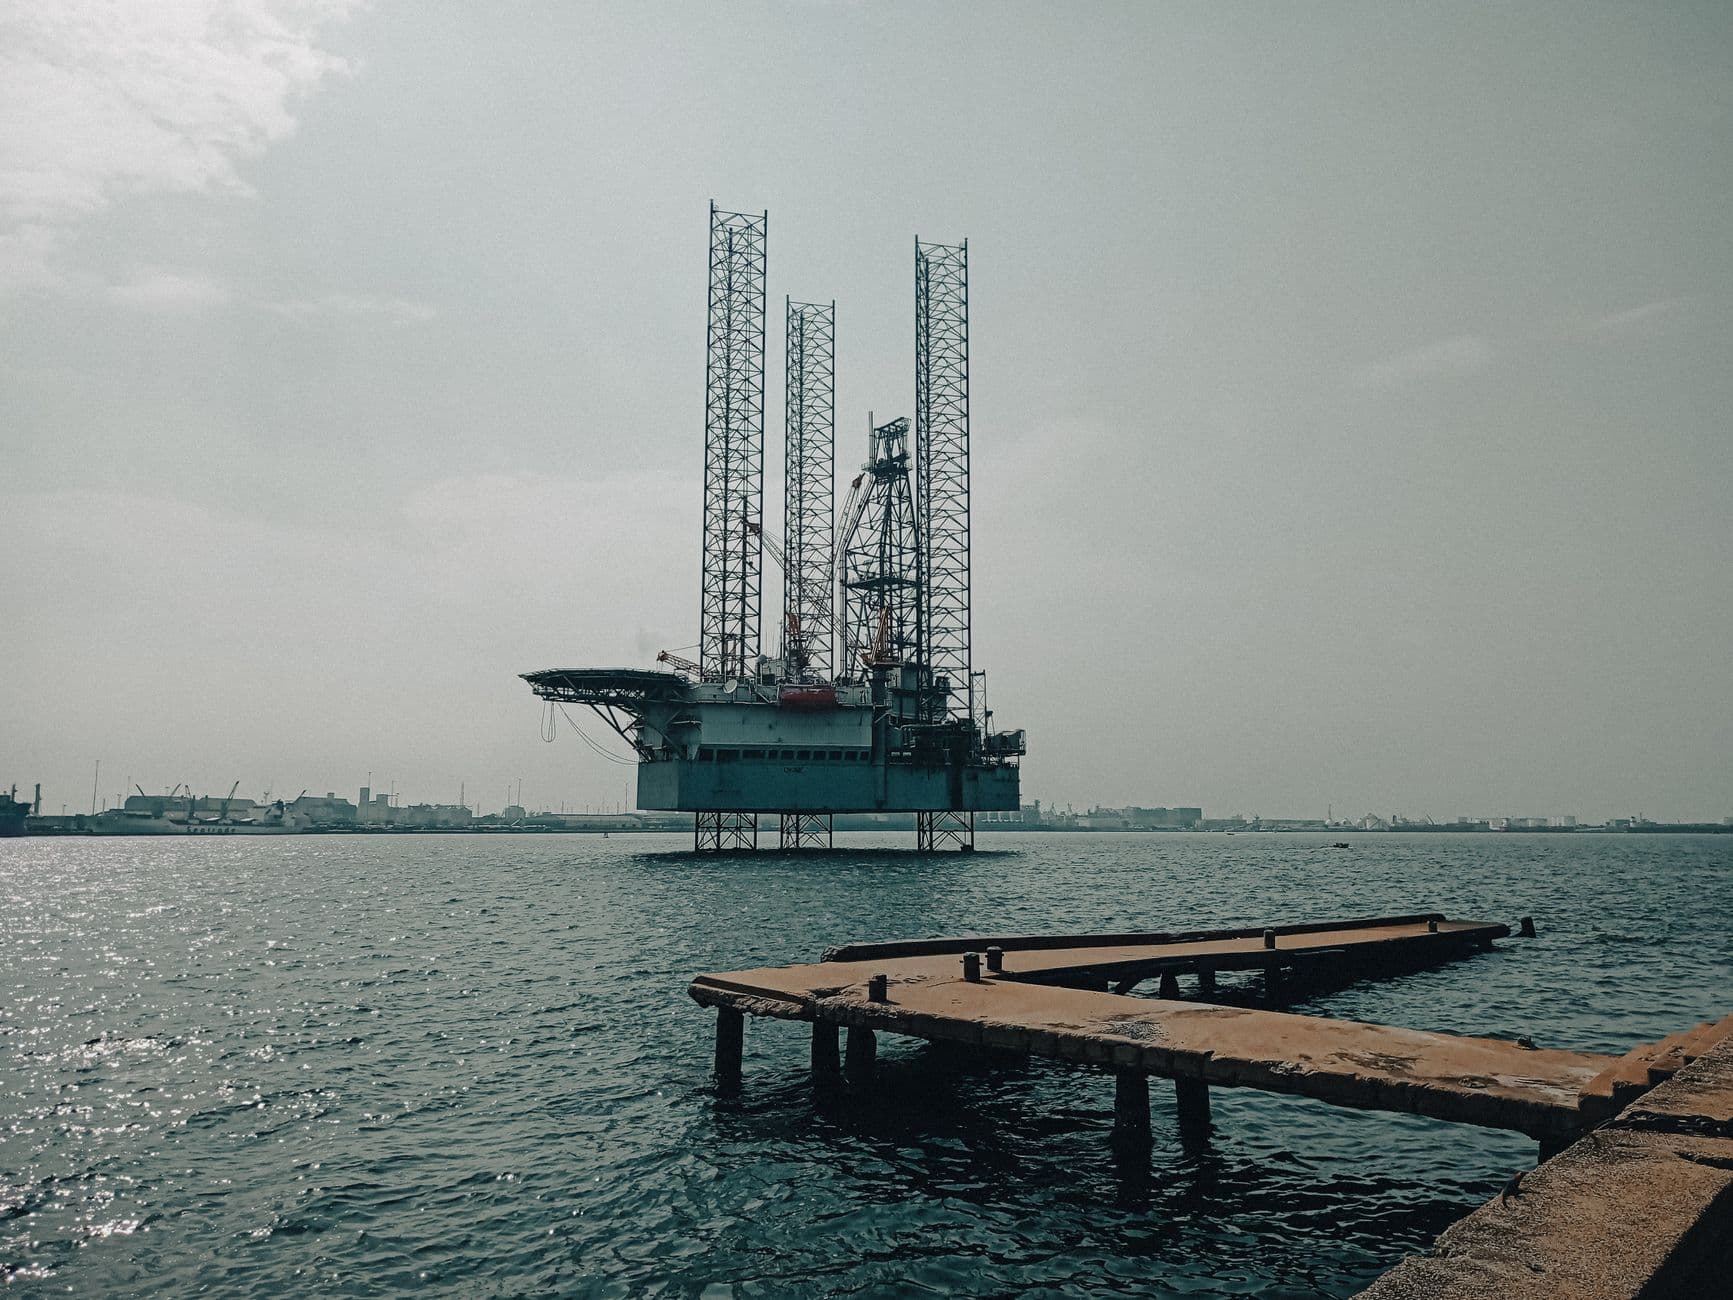
The Register notes that most of Equinor’s oil and gas production takes place offshore Norway, that the company also produces in the UK, the US, Brazil and Canada, and that it employs around 25,000 people in more than 20 countries. The Norwegian state owns 67% of it. Europe has leaned more heavily on Norwegian gas since Russia’s full-scale invasion of Ukraine in 2022, which is why the line about production carries so much weight.
It is still a company statement, made while the incident is live. The claim is that operations and production are unaffected. It does not say the production and corporate networks are fully separate, and it does not say what has been shut down as a precaution. The Register asked Equinor whether any UK operations were affected and whether the attackers got beyond the corporate IT network, and had no answer when it published. In an industrial company the honest answer to those questions usually takes days to establish.
The wider backdrop is a warning from Norway’s own national security authority. The Register reports that only weeks ago, the NSM raised its cyberattack risk assessment to four on a five-point scale, saying successful cyber operations against Norwegian businesses had tripled over the preceding six months and warning of possible disruption to essential services such as water and electricity. That is context, not evidence about this incident. Nobody has linked the two.
#What customers, suppliers and partners should do
Most readers are not Equinor’s IT team. Many will be on the other side of a contract with a large company that is having a bad week. We would do the following, and these are our suggestions, not guidance from Equinor or any authority.
- Work out which of your connections to the affected company are live: shared mailboxes, file transfer, API integrations, federated logins, VPNs, supplier portals. Equinor says it has seen no consequences for partners or suppliers, which is a reason to check calmly, not a reason to skip the check.
- Expect messages that use the incident as cover. When a large firm is publicly in trouble, attackers pose as its staff, its suppliers or its recovery contractors. Tell the people who handle invoices, bank detail changes and password resets that a request which cites the incident gets a call back on a number you already hold.
- Do not rely on email to coordinate with a partner whose email may be down. Agree another route, such as a named person and a phone number, and write it down.
- Ask your own team the question this incident puts to every large organisation: if our corporate email and several business applications were down for several days, how would we tell customers, pay staff and run the shifts? Test the answer, because most plans are written in a document that lives on the systems that would be down.
- Check that your industrial or building controls are separated from the corporate network, and that remote access to them does not share logins with email. Equinor says production is unaffected, but you do not need to be an energy company for this to matter. Our story on flaws in a widely used refrigeration controller is a reminder of the kind of weakness found in industrial controllers.
For a more general planning template, our report on the Microsoft 365 outage from earlier this month shows how a long loss of email and collaboration tools played out for the organisations affected.
#Our view
Equinor’s communications have been clear in one respect: it published a notice on the day it says it detected the attack and has updated the same page three times in two days, each time saying what it does not yet know. That is better practice than the silence that sometimes surrounds these incidents. The weakness is what is missing. A reader who runs a supply chain, a grid connection or a customer service operation that depends on Equinor cannot tell from the statements whether to do anything. We think the company should say, as soon as it can, whether there is any action partners should take, whether any credentials that connect to it should be changed, and whether any of its customer-facing systems are affected.
We expect the incident to run on for days, given that the company says it cannot give a recovery estimate. What would change our view is evidence that production systems were touched, or that data left the company, either of which would turn this from an IT disruption into something much bigger. Equinor says neither has happened so far.
#If you run a small business
A firm that sells to or buys from a large energy company is not likely to be affected directly. The realistic risk is a fake message that mentions Equinor, or invoices that appear to come from it. Ask your IT provider whether your email filtering catches look-alike domains, and phone a known contact before paying a changed bank detail.
#What we do not know
The nature of the attack, how access was gained, when it began, who is responsible, whether any demand has been made, whether internal email is down, and whether UK operations are affected. We will update this story when Equinor, the Norwegian authorities or the police say more.
Evidence trail
Sources and verification
Primary documentation and external technical references used in this article.
About this page
Credited to
Dates
Published
Corrections
No corrections are listed for this page. Some review sweeps corrected pages without naming each one; those are in the corrections log.
Read-only scripts
- Windows devices with no BitLocker recovery key in Entra IDMicrosoft Entra ID, Windows
- Intune devices that haven't synced in N daysMicrosoft Intune
- Mailboxes forwarding to external addressesExchange Online
- BitLocker status of every volume on this PCWindows
Upcoming deadlines
- Intune moves to macOS 15 and laterQ4 2026
- SAP SuccessFactors provisioning: move from basic auth to workload identityNovember 2026
- Intune November release: JIT registration reminder at APNs renewal and automatic JIT for eligible tenantsNovember 2026
Explore KBY
The KBY Brief
A short email about twice a week with new runbooks, configuration traps and fixes from KBY Technologies.
SubscribeMore news
All news
Was this useful?
Reports go to the site owner and are used to correct pages. Corrections are listed at /corrections.
Get new fixes by email.
New runbooks, configuration traps and fixes from KBY Technologies, about twice a week.
Comments
Add a thoughtful note on Equinor Says Its Cyberattack Is Still Under Way Three Days On, With Production Unaffected. Comments are checked for spam and held for moderation before appearing.